How Sentinel Shares Threat Intelligence Across Your Servers
Most server security tools work alone. Sentinel lets every protected server learn from the others: banned IPs go to Queen, get correlated hourly, and are blocked across your fleet.
FixFlex Admin
Founder @ FixFlex LTD, West London
How Sentinel Shares Threat Intelligence Across Your Servers
Most server security tools work alone. Each machine bans the attackers it sees, and the next machine has to learn about the same attacker from scratch. Sentinel's approach is to let every protected server learn from the others. Here's how that works, and what Sentinel does (and deliberately doesn't do) automatically.
The building blocks on each server
Sentinel's security autopilot integrates with three tools that do the actual blocking on every server: Fail2Ban (jail management), CrowdSec (threat intelligence and an HTTP guard) and UFW (firewall rule monitoring).
On top of that, Sentinel detects which services are running and automatically installs Fail2Ban jails for them: sshd, nginx, caddy, apache and mysqld. For MySQL, that means failed logins are caught by a dedicated mysqld jail instead of being left unprotected.
Cross-Fleet IP Reputation: one server's attacker is every server's attacker
This is where the fleet comes in:
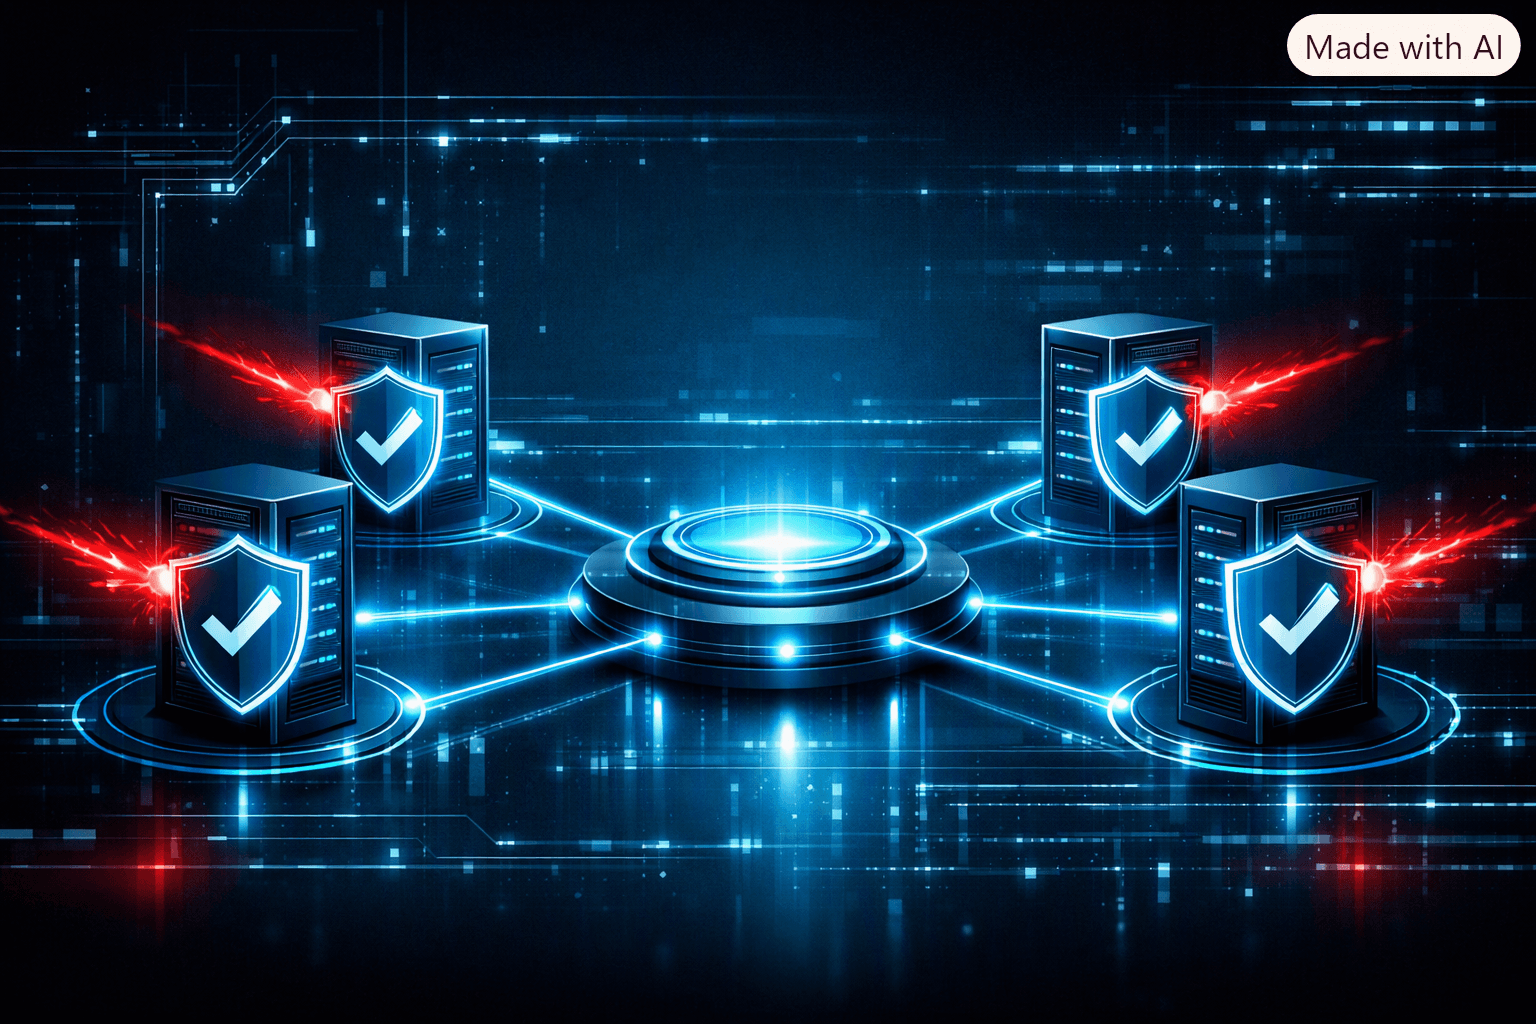
- Each server reports the IPs it has banned to Queen, Sentinel's central server.
- Queen correlates those reports every hour, over the last 7 days, and publishes known attackers as IP-reputation entries.
- On their next sync with Queen, the other servers in your fleet ban those IPs too, before they've tried anything there.
So an IP that hammers SSH on Server A gets blocked on Server B without Server B having to see a single failed login. Cross-Fleet IP Reputation is part of the Enterprise tier ($149/month, up to 10 servers).
What stays a human decision
Some actions are powerful enough that Sentinel leaves them to you:
- Subnet bans. Sentinel does not automatically block whole ranges. If you decide a /24 or /16 needs banning, an admin can do it in Fail2Ban through the AI Chat tool
ban_subnet(Enterprise), as a manual, operator-approved action. - HTTP floods are handled by the Rate Limiting / Active Shield feature (Pro and above), not by the uptime monitor.
Beyond attacks: certificates
Not every risk is an attacker knocking on the door. Sentinel also monitors SSL certificates and alerts you before they expire, so a forgotten renewal doesn't turn into downtime.
Sentinel AI is available in three tiers: - Basic: Free for 1 production server. - Pro: $49/month for up to 5 servers. - Enterprise: $149/month for up to 10 servers, with AI Chat, AI Healer and Cross-Fleet IP Reputation.
Sign up at sentinel-ai.info/pricing to receive a personalised one-line install command (installation takes about 2–4 minutes).
Built by FixFlex Ltd, a London-based AI and web studio.
See your own attack data — Sentinel free tier →
Start FreeComments
No comments yet. Be the first!